API Keys
An Application Programming Interface (API) key lets an external system act on the platform on its own, without a person signing in. Use API keys so trusted partner systems can integrate with your data and operations securely and be shut off individually if one is ever compromised.
What are API Keys?
API keys let external systems interact with the platform, for example:
- Game aggregators
- Payment providers
- Marketing platforms
- Custom integrations
Accessing API Keys
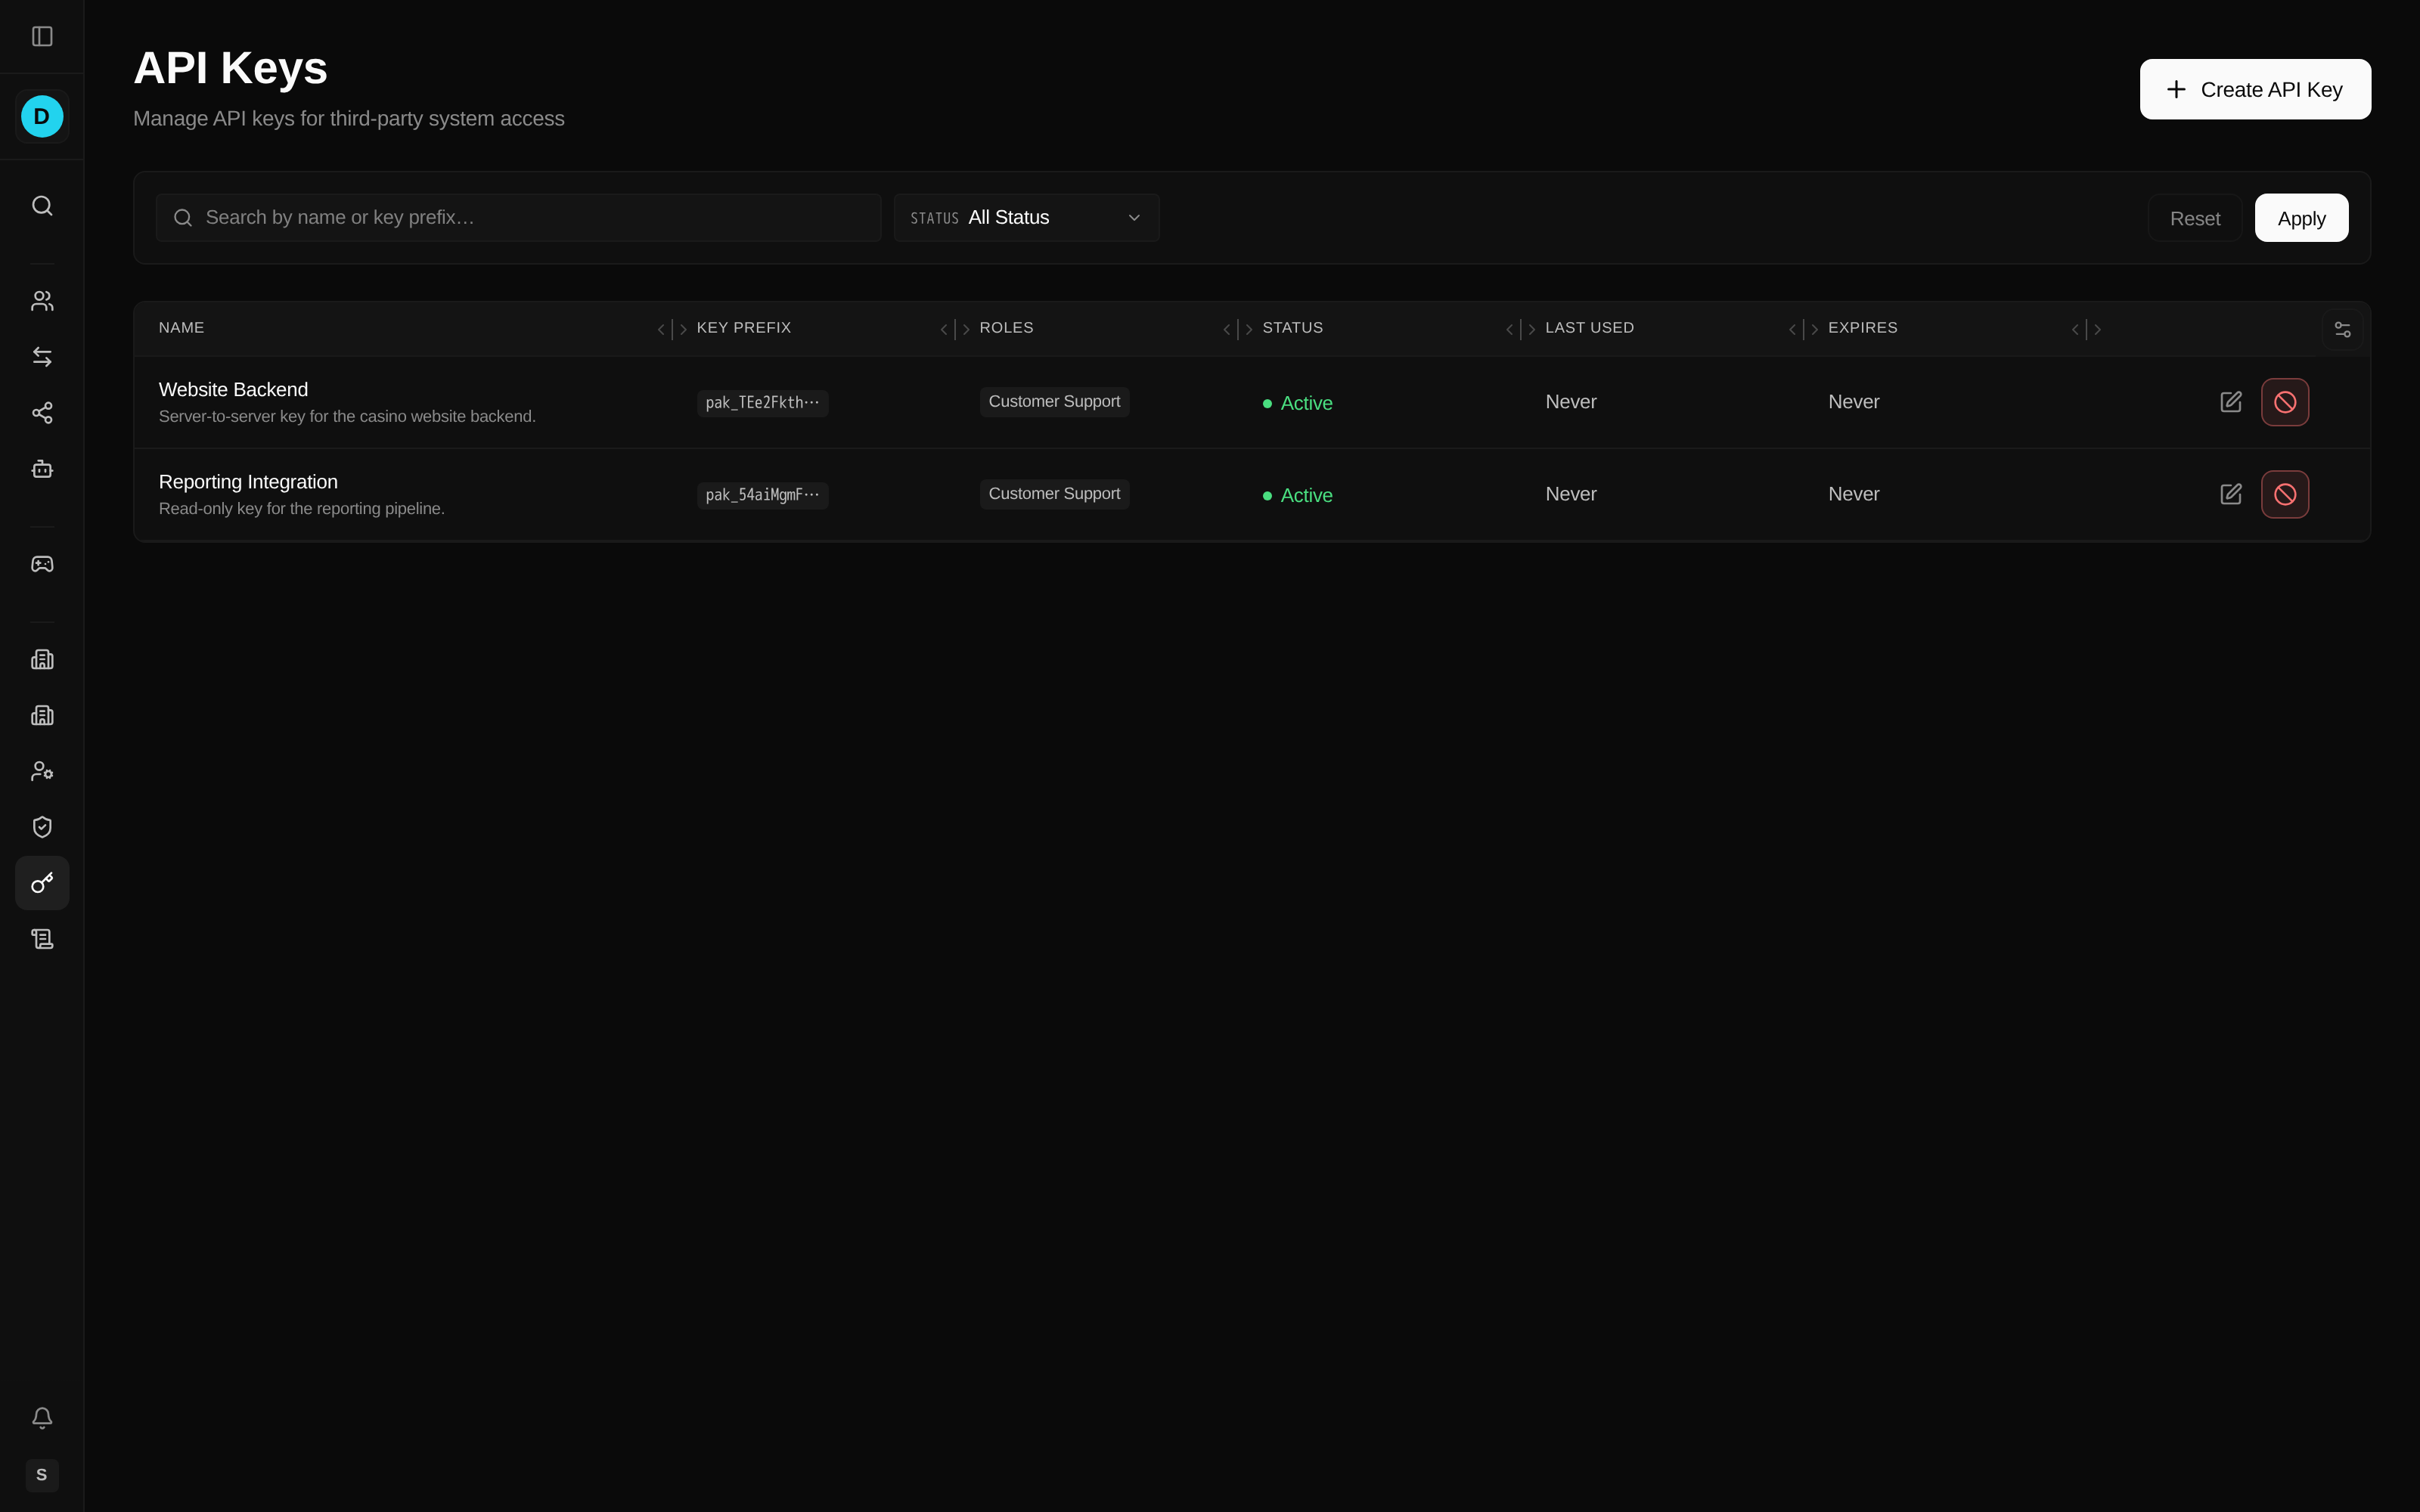
- Open API Keys under the Settings section of the sidebar
- Review existing keys and their status
The list can be searched by name or key prefix, and filtered by status (Active or Revoked).
API Key Properties
| Property | Description |
|---|---|
| Name | Descriptive name for the key |
| Description | Optional free-text note |
| Key Prefix | The visible identifier, shown as <prefix>… (not the full secret) |
| Secret | Private key (shown once on creation) |
| Roles | Roles assigned to the key (roles carry the permissions) |
| Brand Access | The specific brands the key may act on |
| Status | Active or Revoked |
| Expires | Optional expiration date (shown in red once past) |
| Last Used | Most recent API call, with the last-used Internet Protocol (IP) address |
Each key is scoped to an Operator, and the list shows the read-only key prefix as its identifier.
Creating an API Key
Create a key so a specific integration can authenticate as itself, with only the access its role grants.
- Click Create API Key
- Super-admins first select the Operator the key belongs to
- Enter a Name (e.g., "Game Aggregator Production") and an optional Description
- Optionally set an Expiration Date (leave empty for no expiration)
- Assign Roles — the key inherits the permissions of the roles you select
- Choose Brand Access — the brands this key may operate on
- Click Create
The secret is generated and shown exactly once, in a confirmation dialog. Copy it before closing.
Important: Save the Secret
The API secret is shown only once:
- Copy the secret immediately
- Store it securely
- Never share it in plain text
- You cannot retrieve it later
If you lose the API secret, you must revoke the key and create a new one.
API Key Permissions
API keys use the same role system as operator users: a key inherits whatever permissions its assigned roles carry. Give each key only the roles its integration actually needs — for example, a read-only reporting role for an analytics system, or a payments role for a payment gateway — so a leaked key can do as little as possible.
Using API Keys
Authentication Header
Authenticate by sending the full secret in a single header:
X-API-Key: YOUR_API_SECRET
Example Request
curl -X GET "https://api.yourpam.com/api/v1/players" \
  -H "X-API-Key: your_api_secret_here" \
  -H "Content-Type: application/json"
Managing API Keys
Each active key's row shows its status, roles, expiry, and when it was last used (with the last-used IP address), so you can spot unused or unexpected keys at a glance.
Edit a Key
Update a key's name, description, expiration, roles, or brand access as an integration's needs change.
- Find the key in the list
- Click the Edit action on its row
- Change the fields you need and save
Revoke a Key
Immediately cut off a key that is compromised or no longer needed.
- Find the key in the list
- Click Revoke
- Confirm revocation
Revoked keys immediately stop working. This cannot be undone.
Rotate a Key
Replace a key without interrupting a live integration:
- Create a new key with the same roles
- Update the integration with the new key
- Verify the new key works
- Revoke the old key
Rate Limiting
API keys have rate limits:
| Tier | Requests/Minute |
|---|---|
| Public | 100 (per player) |
| System (API key) | 1,000 (per key) |
Exceeding a limit returns a Hypertext Transfer Protocol (HTTP) 429 (Too Many Requests) response.
Security Best Practices
- Minimum permissions - Only grant necessary access
- Separate keys - Use different keys for different integrations
- Rotate regularly - Replace keys periodically
- Monitor usage - Watch for unusual patterns
- Secure storage - Use environment variables or secrets management
- Never commit - Don't store keys in source code
Audit Trail
Each key's row records when it was last used and the IP address of that call, so you can confirm a key is active and being used from where you expect. For a broader history of operator activity, open Audit under the Settings section of the sidebar.
Troubleshooting
Key Not Working
- Verify the key is Active (not Revoked)
- Check the key has required permissions
- Ensure correct authentication header format
- Verify you're using the correct environment (dev/prod)
Rate Limit Exceeded
- Implement request throttling
- Cache responses where appropriate
- Contact support for limit increases
Permission Denied
- Check the key's assigned roles
- Verify the endpoint requires the expected permission
- Update roles if needed